

ISO 27001
Recertification
Internal Audit
Canada
ISO 27001 Recertification Internal Audit in Canada: When to Book and What to Prepare
Preparing for ISO 27001 recertification? Learn when to schedule an independent internal audit, what evidence to prepare, and how to identify three years of ISMS drift before reassessment.
Your Certificate Is Approaching Renewal. Is Your ISMS Still Effective?
Your organization achieved ISO 27001 certification.
You completed surveillance audits.
Your ISMS has been operating for several years.
Now the certificate expiry date is getting closer.
This is not the time to assume:
“We passed surveillance, so we should be fine.”
A lot can change during a three-year certification cycle.
Controls that worked during initial certification may no longer operate in the same way.
That is why an ISO 27001 recertification internal audit should test the current ISMS before the certification body performs its reassessment.
Quick Answer
When Should You Book an Internal Audit Before ISO 27001 Recertification?
Book the internal audit early enough to complete the full improvement cycle.
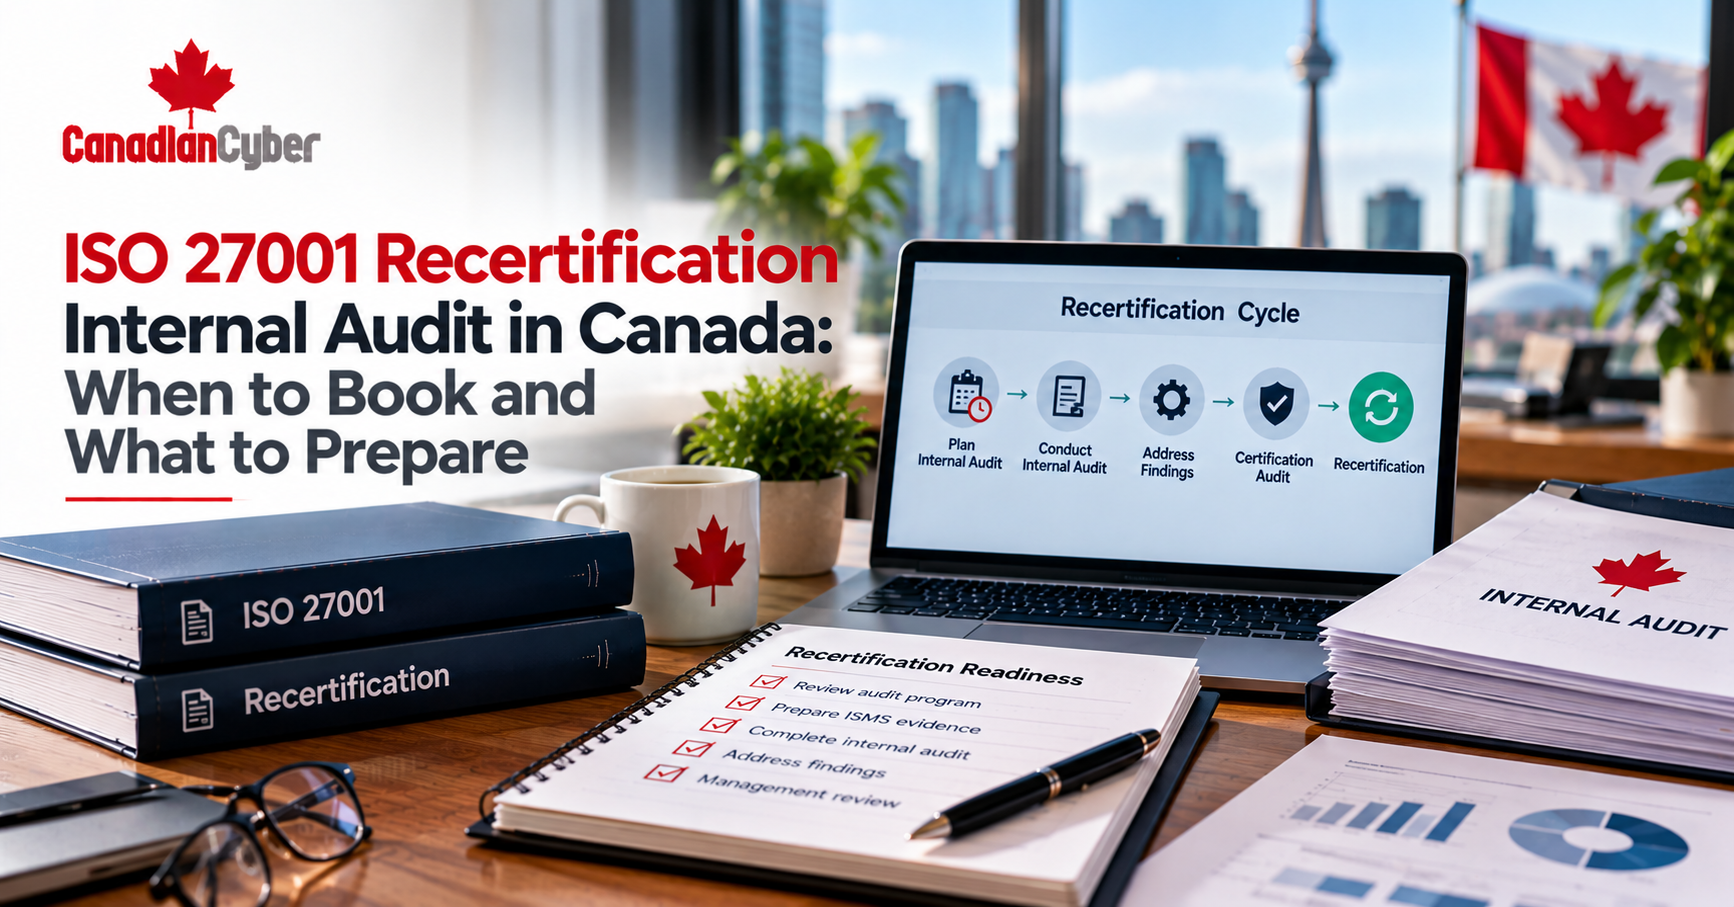
Internal Audit → Findings → Corrective Actions → Retesting → Management Review → Recertification Audit
Do not schedule the internal audit only a few days before the external reassessment.
The exact timing depends on the size and complexity of your ISMS.
However, leave enough time to correct significant findings and prove that important fixes work.
What Is an ISO 27001 Recertification Audit?
Recertification happens near the end of the certification cycle.
It is broader than a normal surveillance audit.
The purpose is to assess whether the management system continues to conform and remains effective enough for certification to continue.
You need to prove more than:
Surveillance vs Recertification: What Changes?
| Area | Surveillance | Recertification |
|---|---|---|
| Purpose | Ongoing conformity | Renew certification cycle |
| Coverage | Selected or sampled areas | Broader management-system reassessment |
| Timing | During certification cycle | Near end of certification cycle |
| Previous Findings | Reviewed | Reviewed across the cycle |
| ISMS Changes | Important | Very important |
| Continual Improvement | Evaluated | Evaluated across the certification cycle |
| Internal Audit Evidence | Relevant | Critical readiness evidence |
Clause 9.2 Still Drives Internal Audit
Internal audit is not only a first-certification activity.
Clause 9.2 requires internal audits at planned intervals.
Your audit program should consider:
- Importance of processes.
- Changes affecting the organization.
- Previous audit results.
- Audit scope.
- Audit criteria.
- Responsibilities.
- Reporting.
- Corrective action.
When Should You Book the Internal Audit?
Work backward from your recertification date.
Do not begin with:
Instead ask:
Example Timeline
| Timing | Activity |
|---|---|
| February | Independent internal audit |
| March | Corrective actions |
| Early April | Retesting and evidence closure |
| Late April | Management review |
| May | Recertification assessment |
The principle is simple: leave enough time to use the internal audit findings.
1. Review the Previous Three Years of Audit Results
Recertification should not be treated like a new certification project.
You already have history.
Review:
- Initial certification findings.
- Surveillance findings.
- Previous internal audits.
- Observations.
- Opportunities for improvement.
- Corrective actions.
- Repeat findings.
For example:
2. Verify Previous Corrective Actions
Do not rely only on a status field saying “Closed.”
Select previous findings and retest the correction.
Previous finding:
Supplier security reviews were inconsistent.
Corrective action:
Annual supplier review workflow implemented.
Internal audit test:
Sample critical suppliers and verify that reviews, risk decisions, evidence, and follow-up actions exist.
The goal is to determine whether the fix stayed effective.
3. Review Changes Since Certification
One of the biggest recertification risks is ISMS drift.
Compare your organization today with the organization that originally achieved certification.
Have you added:
4. Recheck the ISMS Scope
Your scope may have made sense three years ago.
Does it still reflect the business today?
Review:
- Locations.
- Services.
- Products.
- Teams.
- Systems.
- Networks.
- Cloud environments.
- Interfaces.
- Outsourced processes.
- Exclusions.
5. Refresh the Risk Assessment
Risk registers often become stale after certification.
Check whether your assessment reflects:
- New threats.
- New technology.
- New suppliers.
- Security incidents.
- Regulatory changes.
- Customer requirements.
- Cloud changes.
- AI adoption.
- Significant organizational changes.
Also review:
- Risk owners.
- Treatment decisions.
- Due dates.
- Accepted risks.
- Overdue actions.
Has Your ISMS Drifted During the Certification Cycle?
Canadian Cyber can independently review your current ISMS before recertification and test whether risks, controls, evidence, previous findings, and corrective actions remain effective.
Find three years of control drift before the recertification auditor does.
6. Review the Statement of Applicability
The Statement of Applicability should still align with your current risks and controls.
Check:
- Control applicability.
- Control justifications.
- Implementation status.
- Control owners.
- Supporting evidence.
- Changes since certification.
Do not treat the SoA as a document that was finished three years ago and never touched again.
7. Test Access Control Across the Certification Cycle
Access-control drift is common.
Sample:
- Joiners.
- Movers.
- Leavers.
- Privileged users.
- Contractors.
- Service accounts.
- Administrative accounts.
- Access reviews.
Look especially for:
- Former employees.
- Old vendor accounts.
- Excessive privileged access.
- Dormant accounts.
- Unowned service accounts.
- Repeated overdue access reviews.
8. Review Supplier Changes
Your supplier environment may look very different from three years ago.
Review:
- Supplier inventory.
- Criticality.
- Security assessments.
- Contracts.
- DPAs.
- Assurance reports.
- Supplier incidents.
- Review dates.
Prioritize suppliers that:
- Handle sensitive data.
- Host production services.
- Provide security-critical software.
- Support important business operations.
9. Review Incidents and Lessons Learned
Recertification gives you a useful window for testing continual improvement.
For significant incidents, ask:
- Was the root cause identified?
- Were corrective actions implemented?
- Did risks change?
- Were controls retested?
- Were lessons learned?
- Did similar incidents happen again?
10. Review Vulnerability and Patch Management
Look at trends, not only today’s scanner dashboard.
Ask:
- Are critical vulnerabilities remediated on time?
- Are exceptions controlled?
- Are overdue items increasing?
- Do findings have owners?
- Are fixes verified?
- Are unsupported systems still present?
11. Test Backup and Recovery Again
A backup report does not prove recovery.
Review:
- Backup coverage.
- Failed backups.
- Restore tests.
- Recovery evidence.
- Recovery objectives.
- Business continuity changes.
If critical systems changed during the certification cycle, backup and recovery coverage should have changed with them.
12. Review Security Objectives and Metrics
Security objectives can become forgotten after certification.
Check whether:
- Objectives remain relevant.
- Metrics are measured.
- Owners are assigned.
- Results are reviewed.
- Missed targets lead to action.
Recertification should show that the ISMS has been managed, not merely maintained on paper.
13. Review the Internal Audit Program Itself
Do not audit only the security controls.
Audit the audit program too.
- Did planned audits happen?
- Were higher-risk areas audited appropriately?
- Were organizational changes reflected in the program?
- Were previous findings considered?
- Were competent auditors used?
- Were results reported to management?
- Were corrective actions tracked?
If the internal audit program itself has gaps, address them before recertification.
14. Protect Auditor Objectivity
The internal audit does not always need to be outsourced.
However, objectivity and impartiality should be protected.
That can become difficult when the same person:
- Built the ISMS.
- Maintains the risk register.
- Implements controls.
- Collects evidence.
- Then audits all the same activities.
An independent external internal auditor may make sense when:
- Your internal team designed most of the ISMS.
- Recertification is approaching.
- Management wants independent assurance.
- Previous findings require retesting.
- Internal audit resources are limited.
What Evidence Should You Prepare?
A recertification-focused audit should use both current evidence and historical evidence from the certification cycle.
Core ISMS Documents
- Current ISMS scope.
- Risk assessment.
- Risk treatment plan.
- Statement of Applicability.
- Information security policy.
- Security objectives.
- Asset inventory.
Audit and Governance Evidence
- Internal audit program.
- Internal audit reports.
- Surveillance audit reports.
- Previous external findings.
- Corrective-action register.
- Management review records.
- Monitoring results.
Operational Evidence
- Access reviews.
- Joiner and leaver samples.
- Supplier assessments.
- Vulnerability reports.
- Patch records.
- Incident records.
- Backup and restore tests.
- Change records.
- Training evidence.
- Logging and monitoring records.
- Secure-development evidence.
Change Evidence
- New offices.
- New products.
- New cloud platforms.
- New suppliers.
- Major migrations.
- Acquisitions.
- New AI services.
ISO 27001 Recertification Internal Audit Checklist
Before the external reassessment, confirm:
☐ Current ISMS scope reflects the business.
☐ Risk assessment is current.
☐ Risk treatments are progressing.
☐ SoA reflects current control decisions.
☐ Previous external findings were addressed.
☐ Previous internal findings were addressed.
☐ Corrective actions were verified.
☐ Significant organizational changes entered the ISMS.
☐ Access reviews are current.
☐ Privileged access is controlled.
☐ Suppliers were reassessed.
☐ Vulnerabilities and exceptions are managed.
☐ Incidents produced lessons learned.
☐ Backup and recovery evidence is current.
☐ Policies were reviewed.
☐ Security objectives were measured.
☐ Internal audit coverage is complete.
☐ Management review reflects current performance.
☐ Open risks and actions have owners.
☐ Evidence can be retrieved quickly.
Common Recertification Readiness Gaps
The organization changed, but the scope, risks, and controls did not.
Corrective actions exist, but effectiveness is unclear.
Recurring issues may indicate weak root-cause analysis.
New technologies, suppliers, and business risks are missing.
Control decisions still reflect the original implementation.
The same checklist is repeated without considering changing risk.
Controls operate, but evidence is difficult to retrieve.
Minutes show discussion but not clear decisions, owners, or follow-up.
Recertification vs First Certification: What Should Internal Audit Do Differently?
For first certification, the audit often asks:
Before recertification, the stronger question is:
Therefore, look for trends.
Was an access review completed?
Also ask:
Were access reviews consistently completed across the cycle?
Does a risk register exist?
Also ask:
Did it change when the business changed?
Was a finding closed?
Also ask:
Did the problem stay fixed?
Want an Independent Readiness View Before Recertification?
Canadian Cyber can test your current ISMS, previous findings, control evidence, risk register, Statement of Applicability, access controls, suppliers, corrective actions, and management-review readiness.
Request an ISO 27001 Recertification Internal Audit Consultation
Frequently Asked Questions
How often does ISO 27001 recertification happen?
Certification commonly follows a three-year cycle, with surveillance during the cycle and recertification toward the end.
Do we need an internal audit before recertification?
Organizations need to maintain their Clause 9.2 internal audit program throughout the certification cycle. Before recertification, make sure relevant audit coverage is complete and significant findings are addressed.
How early should we book the internal audit?
Book it early enough to complete corrective actions and verify important fixes before the recertification assessment.
Is recertification the same as surveillance?
No. Surveillance supports confidence during the certification cycle. Recertification occurs near the end of the cycle and supports renewal into a new certification period.
Can we use an external provider for the internal audit?
Yes. An external provider can perform an internal audit on behalf of the organization when appropriate competence, objectivity, and impartiality are maintained.
What should we do with open findings before recertification?
Prioritize them according to risk and significance.
Maintain an owner, corrective action, target date, current status, interim controls where required, and verification evidence.
What if our organization changed significantly during the certification cycle?
Make sure those changes are reflected in the scope, risks, SoA, assets, suppliers, controls, objectives, and internal-audit coverage.
The Takeaway
Recertification is not simply:
It asks whether your ISMS remained alive.
A strong recertification-readiness sequence looks like:
Review the Three-Year Cycle
↓
Independent Internal Audit
↓
Corrective Actions
↓
Verify Important Fixes
↓
Management Review
↓
Recertification Audit
Use internal audit to identify control drift while there is still time to fix it.
Preparing for ISO 27001 Recertification in Canada?
Canadian Cyber helps organizations independently review their ISMS before ISO 27001 recertification.
Our internal audit support can include:
- Full ISO 27001 internal audits.
- Recertification-readiness testing.
- Previous finding verification.
- Risk register and SoA review.
- Access-control sampling.
- Supplier evidence review.
- Vulnerability and incident evidence.
- Corrective-action verification.
- Management-review readiness.
- Audit evidence organization.
Book Your Independent ISO 27001 Internal Audit Before Recertification
Stay Connected With Canadian Cyber
Follow Canadian Cyber for practical guidance on ISO 27001 internal audits, recertification, surveillance readiness, certification, risk management, and ISMS improvement.