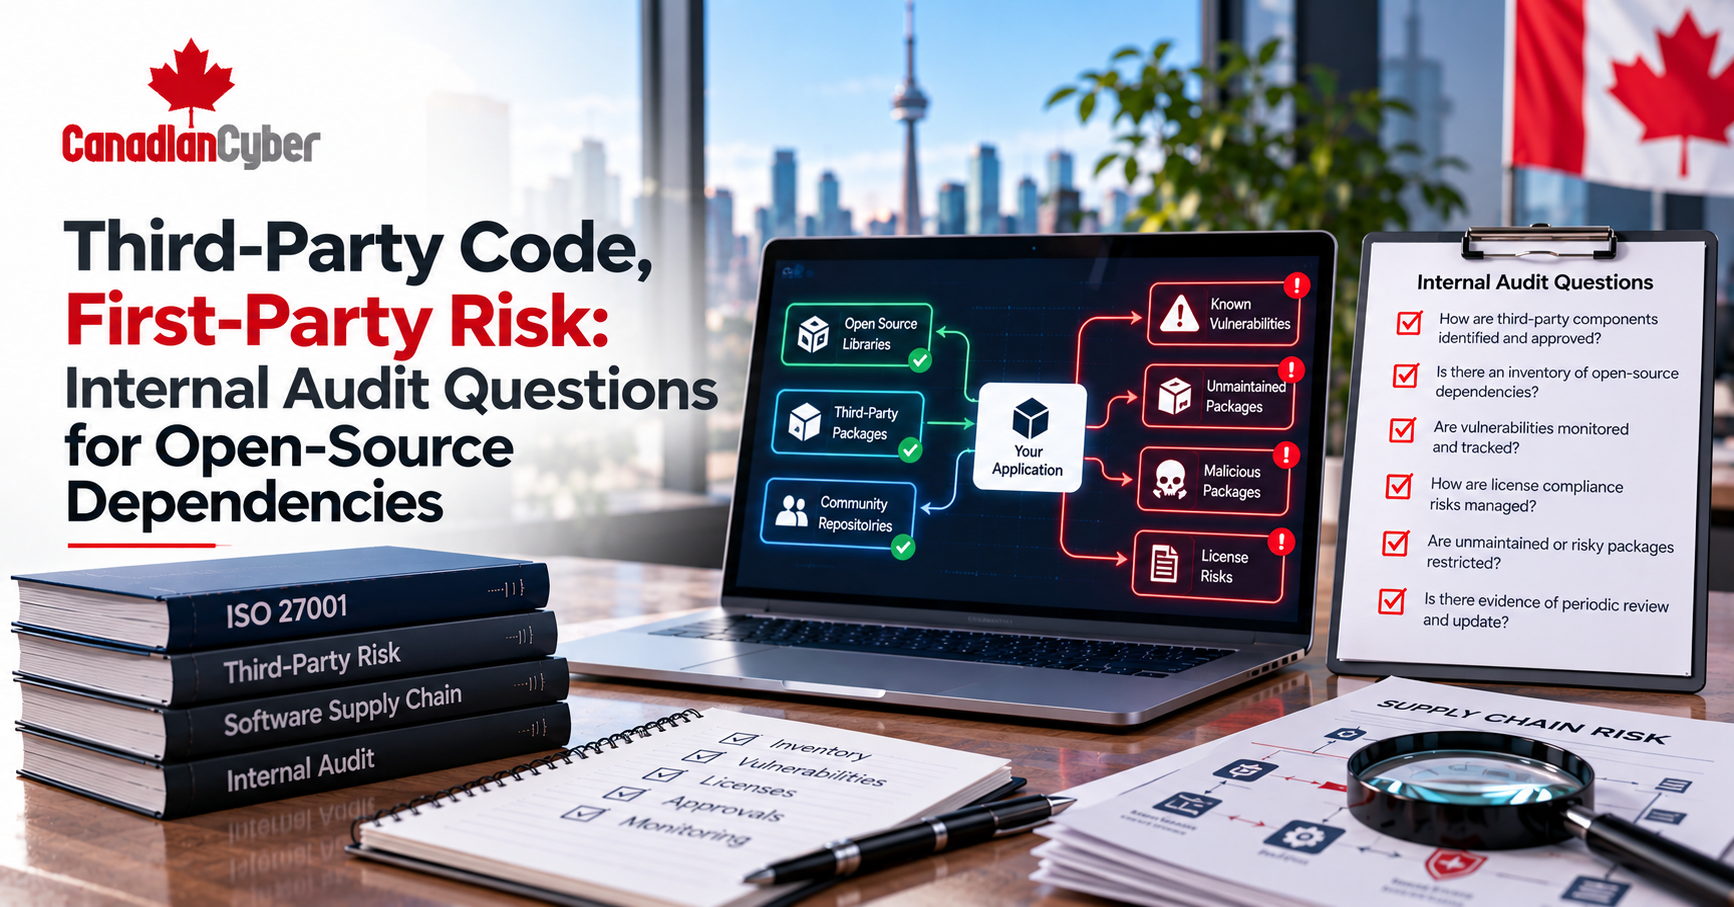
Third-Party Code, First-Party Risk
Open-source code may come from third parties, but the security risk becomes yours once it enters your application. Learn how ISO 27001 internal auditors can review dependencies, vulnerabilities, package provenance, project health, SBOM coverage, ownership, version controls, and software supply chain risk.

0 Comment

Rafia Rizwan