

ISO 27001
Gap Assessment
Internal Audit
Canada
ISO 27001 Gap Assessment vs Internal Audit in Canada: Which Should You Book Before Certification?
Not sure whether you need an ISO 27001 gap assessment or internal audit? Learn what each review does, which one is required, and when Canadian organizations should book each service.
Gap Assessment or Internal Audit: Why the Difference Matters
You are working toward ISO 27001 certification.
Your policies are being written.
Your risk register is taking shape.
Controls are being implemented.
Then someone asks:
Should we book a gap assessment or an internal audit?
They may sound similar.
However, they serve different purposes.
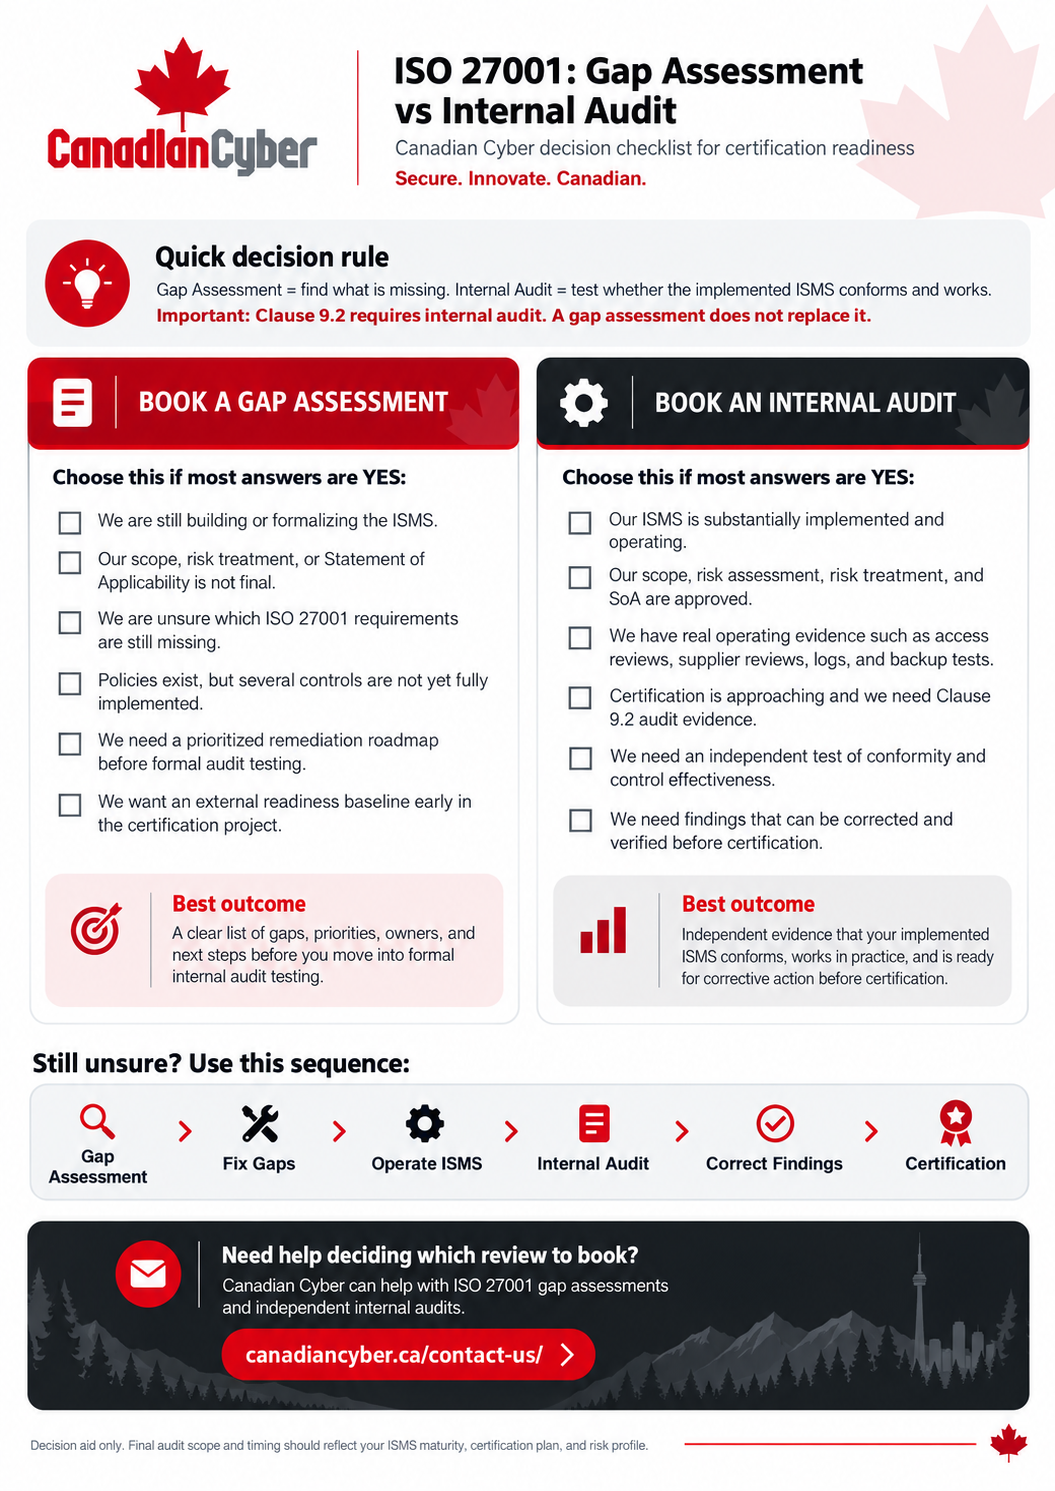
A gap assessment helps you understand what is still missing.
An internal audit tests whether the ISMS you implemented actually conforms and works.
A gap assessment is generally optional. Internal audit is part of ISO 27001 Clause 9.2 requirements.
Quick Answer
Should You Book an ISO 27001 Gap Assessment or Internal Audit?
Book a Gap Assessment
Choose this when ISO 27001 implementation is still underway and you need to identify missing requirements, controls, processes, or evidence.
Book an Internal Audit
Choose this when your ISMS is substantially implemented and you need independent testing of conformity and control effectiveness.
For first-time certification, some organizations benefit from both.
Gap Assessment → Remediation → Implementation → Internal Audit → Corrective Actions → Management Review → Certification Audit
What Is an ISO 27001 Gap Assessment?
An ISO 27001 gap assessment compares your current management system against ISO/IEC 27001:2022 requirements.
Its main purpose is diagnostic.
It helps identify:
- Requirements already addressed.
- Requirements only partly implemented.
- Missing documentation.
- Missing processes.
- Weak control implementation.
- Evidence still required.
- Areas requiring remediation before certification.
What Is an ISO 27001 Internal Audit?
An internal audit usually happens later in the implementation process.
Clause 9.2 requires internal audits at planned intervals.
The auditor should test whether the ISMS:
- Conforms to the organization’s requirements.
- Conforms to relevant ISO 27001 requirements.
- Is effectively implemented.
- Is effectively maintained.
That means the auditor does more than look for missing documents.
Access reviews happen quarterly.
Auditor asks:
Show me the last quarterly access review.
Terminated users lose access.
Auditor tests:
A sample of recent departures.
Vendors receive security reviews.
Auditor checks:
Actual supplier evidence.
Controls are implemented.
Auditor tests:
Whether those controls actually operate.
ISO 27001 Gap Assessment vs Internal Audit: Simple Comparison
| Area | Gap Assessment | Internal Audit |
|---|---|---|
| Main Purpose | Find what is missing | Test conformity and effectiveness |
| Best Timing | Earlier in implementation | After substantial implementation |
| Required by Clause 9.2? | No | Yes |
| Tests Operational Evidence | May, depending on scope | Yes |
| Typical Output | Readiness gaps | Audit findings / nonconformities |
| Helps Implementation | Yes | Not the primary purpose |
| Supports Certification Readiness | Yes | Yes |
| Replaces Internal Audit | No | Not applicable |
| Best Question | What do we still need? | Does our ISMS actually work? |
When Should You Book a Gap Assessment?
A gap assessment makes the most sense while implementation is still underway.
Consider one when:
- Your organization is new to ISO 27001.
- You inherited an incomplete ISMS.
- Your team is unsure which requirements remain.
- Policies exist, but controls are inconsistent.
- Your certification scope is still being finalized.
- You want an independent readiness baseline.
- Leadership needs a remediation roadmap.
- You are moving from informal security practices to a formal ISMS.
Example
A 70-person Canadian SaaS company already has:
- Security policies.
- Microsoft 365 controls.
- An asset inventory.
- Some supplier assessments.
- Basic incident-response procedures.
However, it does not yet have:
- A complete Statement of Applicability.
- Formal risk treatment evidence.
- A finished internal audit program.
- Management review.
- Complete operating evidence.
In this case, a gap assessment may be more useful before booking the formal internal audit.
When Should You Book an Internal Audit?
Book an internal audit when the ISMS is mature enough to be tested.
Ideally, you already have:
- A defined ISMS scope.
- A current risk assessment.
- A risk treatment plan.
- A Statement of Applicability.
- Approved policies and procedures.
- Implemented controls.
- Operating evidence.
- Control owners.
- An asset inventory.
- Supplier-management evidence.
- Incident records where applicable.
- Access-management evidence.
- Monitoring evidence.
Which Review Is Required Before Certification?
Gap Assessment
A gap assessment is a readiness activity. It is generally optional and helps identify missing implementation work.
Internal Audit
Internal audit is part of the ISO 27001 management-system requirements under Clause 9.2.
Not Sure Which ISO 27001 Review You Need?
Canadian Cyber can help determine whether your current ISMS maturity calls for a gap assessment, an independent internal audit, or both.
The goal is to choose the right review at the right stage instead of paying for work that does not match your current readiness.
Can You Skip the Gap Assessment?
Yes, in many cases.
You may not need a separate gap assessment if:
- Your team understands the ISO 27001 requirements.
- Implementation is substantially complete.
- Your Statement of Applicability is current.
- Evidence is organized.
- Control owners understand their responsibilities.
- You already have a clear remediation list.
In this situation, moving to the internal audit may provide more value.
When Should You Use Both?
Many first-time certification projects benefit from both services.
Gap Assessment
Remediation
Run the ISMS
Internal Audit
Corrective Actions
Verify Important Fixes
Management Review
Certification Audit
Avoid using the internal audit as the first time anyone seriously reviews your implementation.
What Does a Gap Assessment Usually Test?
ISMS Scope
Is the certification boundary clear?
Organizational Context
Have relevant internal and external issues been considered?
Interested Parties
Are important stakeholder requirements understood?
Risk Assessment
Is there a defined methodology and current risk assessment?
Risk Treatment
Are risks linked to treatment decisions?
Statement of Applicability
Are Annex A decisions documented and justified?
Policies and Procedures
Are required processes defined?
Control Implementation
Are important controls being implemented?
Evidence Readiness
Will you be able to prove the controls operate?
What Does the Internal Audit Test?
Internal audit should go further by sampling operating evidence.
Are joiners, movers, leavers, and access reviews operating?
Are risks current, owned, treated, and reviewed?
Are critical suppliers assessed and monitored?
Are findings identified, prioritized, remediated, and verified?
Are incidents recorded, investigated, and used for improvement?
Can successful restoration be demonstrated?
Are code access, CI/CD, changes, and security testing controlled?
Are objectives, audits, monitoring, and corrective actions effective?
Do You Need an Independent Internal Auditor?
Internal audit does not always need to be outsourced.
However, objectivity and impartiality matter.
Consider a compliance manager who:
- Designed the ISMS.
- Wrote the policies.
- Created the risk register.
- Implemented the controls.
- Collected the evidence.
If the same person then audits all of that work, a self-review concern may arise.
Which Service Should a Canadian Organization Choose?
Scenario 1: Early Implementation
Major pieces are still missing.
Book: Gap Assessment
Scenario 2: Almost Complete
Risks, controls, SoA, policies, and evidence are substantially ready.
Book: Internal Audit
Scenario 3: Readiness Is Unclear
Your team believes implementation is complete, but nobody independent has checked.
Consider: Gap Assessment, then Internal Audit.
What Should You Prepare for a Gap Assessment?
Prepare what you already have.
- Proposed ISMS scope.
- Current policies.
- Existing risk assessment.
- Current control documentation.
- Asset inventory.
- Supplier information.
- Technology overview.
- Implementation plan.
- Certification timeline.
Your ISMS does not need to be perfect. Finding what is incomplete is the purpose of the assessment.
What Should You Prepare for an Internal Audit?
For an internal audit, prepare operational evidence.
- Final or approved ISMS scope.
- Risk assessment.
- Risk treatment plan.
- Statement of Applicability.
- Policies and procedures.
- Asset inventory.
- Access reviews.
- Security-awareness evidence.
- Supplier reviews.
- Vulnerability-management evidence.
- Incident records.
- Backup tests.
- Change records.
- Secure-development evidence where applicable.
- Monitoring results.
- Corrective-action records.
Common Mistake: Booking the Internal Audit Too Early
An internal audit can lose value if major implementation work is still unfinished.
For example:
- The Statement of Applicability is unfinished.
- The risk assessment is incomplete.
- No access reviews have occurred.
- Supplier-security evidence is missing.
- No backup restoration test has occurred.
- Management-system monitoring is incomplete.
- Core controls are still being deployed.
In this situation, a gap assessment may provide more practical value first.
Common Mistake: Booking Another Gap Assessment Too Late
The opposite problem can also happen.
Your ISMS is implemented.
Evidence exists.
Certification is approaching.
However, the organization books another readiness review instead of the required internal audit.
Gap Assessment Findings vs Internal Audit Findings
Gap Assessment Finding
“Access review process is not fully implemented.”
Internal Audit Finding
“Quarterly access reviews are required by procedure AC-04. However, no Q3 review was completed for Microsoft Entra ID.”
The internal audit finding is based on defined criteria and operating evidence.
What Should You Ask a Provider Before Booking?
- Which service do you recommend at our maturity level?
- What will you test?
- Will you review operating evidence?
- Will you interview control owners?
- What will the report contain?
- How will findings be classified?
- Will the internal audit address Clause 9.2 requirements?
- How do you protect auditor independence?
- Can corrective actions be retested?
- Can the work be performed remotely?
- What information do you need before quoting?
ISO 27001 Gap Assessment vs Internal Audit Decision Checklist
Book a Gap Assessment if:
- You are early or midway through implementation.
- You are unsure what requirements remain.
- Your SoA or risk treatment is incomplete.
- Evidence is still being built.
- You need a remediation roadmap.
- You want an independent readiness baseline.
Book an Internal Audit if:
- Your ISMS is substantially implemented.
- Policies and procedures are approved.
- Applicable controls are operating.
- Evidence exists.
- Certification is approaching.
- You need Clause 9.2 audit coverage.
- You need independent control-effectiveness testing.
Consider Both if:
- This is your first certification.
- Your team has limited ISO 27001 experience.
- Your environment is complex.
- Significant gaps are likely.
- You want diagnostics followed by formal audit testing.
Still Unsure Which Review to Book?
Tell Canadian Cyber where you are in your ISO 27001 journey. We can help determine whether you need a gap assessment, an independent internal audit, or a staged approach using both.
Book an ISO 27001 Gap Assessment or Internal Audit Consultation
Frequently Asked Questions
Is an ISO 27001 gap assessment required before certification?
No. A separate gap assessment is generally optional. It is a readiness activity used to identify missing implementation work.
Is an ISO 27001 internal audit required?
Yes. Clause 9.2 requires organizations to perform internal audits at planned intervals.
Can a gap assessment replace an internal audit?
No. A gap assessment identifies implementation gaps. An internal audit tests the implemented management system against audit criteria and evidence.
Which should happen first?
If implementation is incomplete, perform the gap assessment first. If the ISMS is substantially implemented, you may be ready for internal audit.
Can the same company perform the gap assessment and internal audit?
Potentially. However, independence and objectivity should be considered carefully for the internal audit.
Can an ISO 27001 internal audit be outsourced in Canada?
Yes. A competent external provider can perform an internal audit on behalf of the organization when appropriate objectivity is maintained.
How long before certification should the internal audit happen?
Schedule it early enough to address findings and verify important corrective actions before the certification audit.
What if our gap assessment identifies major problems?
Prioritize the gaps, assign owners, complete remediation, collect operating evidence, and then conduct the internal audit once the ISMS is sufficiently implemented.
The Takeaway
An ISO 27001 gap assessment and internal audit can both be valuable.
However, they solve different problems.
For many first-time certification projects, the stronger path is:
Gap Assessment
↓
Implement and Fix Gaps
↓
Operate the ISMS
↓
Independent Internal Audit
↓
Corrective Actions
↓
Management Review
↓
Certification Audit
Do not use a gap assessment as a substitute for internal audit.
Also, do not waste an internal audit on an ISMS that is clearly still under construction.
Not Sure Which ISO 27001 Review You Need?
Canadian Cyber supports Canadian organizations from early ISO 27001 implementation through certification readiness.
Support can include:
- ISO 27001 gap assessments.
- ISMS scoping.
- Risk assessment and treatment.
- Implementation support.
- Independent internal audits.
- Management review support.
- Certification-readiness reviews.
- Corrective-action support.
If your ISMS is still being built, we can help identify the gaps. If implementation is complete, we can independently test whether it is ready for certification.
Book an ISO 27001 Gap Assessment or Independent Internal Audit with Canadian Cyber
Stay Connected With Canadian Cyber
Follow Canadian Cyber for practical guidance on ISO 27001 implementation, internal audits, certification readiness, risk management, and ISMS improvement.