

ISO 27001
Internal Audit
Canada
Certification Readiness
ISO 27001 Internal Audit Quote in Canada: What to Prepare Before Hiring an Auditor
Looking for an ISO 27001 internal audit quote? Prepare the right information before contacting an auditor so your proposal reflects your real ISMS scope, complexity, timeline, and audit needs.
Request Your ISO 27001 Internal Audit Quote from Canadian Cyber
Before You Ask “How Much Does an ISO 27001 Internal Audit Cost?”
You have implemented your ISMS.
Your certification audit is getting closer.
Now you need an independent internal audit.
Naturally, one of the first questions is:
How much does an ISO 27001 internal audit cost?
However, an auditor needs context before giving you a meaningful proposal.
A 25-person SaaS company is very different from a 500-person multi-location organization.
The better question is:
What information should we provide so the auditor can accurately scope the engagement?
This guide explains exactly what to prepare before requesting your ISO 27001 internal audit quote.
Quick Answer
What Information Is Needed for an ISO 27001 Internal Audit Quote?
Prepare these five details first:
What is included in the certification boundary?
How many people fall within scope?
Where does your organization operate?
When are Stage 1, Stage 2, or surveillance audits planned?
What exactly do you want the auditor to deliver?
It also helps to explain your ISMS maturity, technology, suppliers, evidence readiness, and whether follow-up testing is required.
Why ISO 27001 Internal Audit Quotes Vary
There is no useful one-price-fits-all ISO 27001 internal audit.
Audit effort depends on the size and complexity of the ISMS.
Company A
- 30 employees.
- One Canadian office.
- Microsoft 365 and Azure.
- One main SaaS product.
- Clearly defined ISMS scope.
- Organized evidence.
Company B
- 450 employees.
- Four offices.
- International remote workers.
- Multiple production platforms.
- Several business units.
- Large supplier ecosystem.
Both companies may need an ISO 27001 internal audit. However, the required audit effort will be very different.
1. Prepare Your ISMS Scope
Start with the ISMS scope.
Your scope tells the auditor what falls inside the audit boundary.
Example Scope
Provide information about:
- Your formal ISMS scope statement.
- Locations included in scope.
- Major business processes.
- Important systems.
- Cloud platforms.
- Relevant departments.
- Significant exclusions.
If the scope is still being finalized, tell the auditor.
2. Provide Your Employee Count
Tell the auditor your total employee count.
Then identify how many employees are inside the ISMS scope.
Total employees: 220
Employees within ISMS scope: 85
These numbers may be different.
Employee count helps the auditor understand interview, sampling, access-control, awareness, HR-security, and offboarding complexity.
3. Explain Your Locations and Working Model
Tell the auditor where your organization operates.
For example:
- Toronto headquarters.
- Vancouver office.
- Remote employees across Canada.
- Development team in another country.
Also explain whether employees are:
Remote
Hybrid
Location information can affect remote delivery, onsite work, physical-security testing, and regional audit sampling.
4. Share Your Certification Timeline
This is one of the most important details.
Tell the auditor:
- Your Stage 1 audit date.
- Your Stage 2 audit date.
- Your surveillance audit date.
- Your recertification date, if applicable.
Avoid saying only:
Provide actual dates where possible.
A clear timeline helps the auditor plan interviews, reporting, and follow-up.
Ready to Scope Your ISO 27001 Internal Audit?
Send Canadian Cyber your ISMS scope, employee count, locations, certification timeline, and audit expectations. We can use that information to understand the engagement and prepare the next steps.
Request Your ISO 27001 Internal Audit Quote from Canadian Cyber
5. Explain Whether This Is Your First Internal Audit
A first certification audit may require a different approach from a mature annual audit.
If this is your first audit, say so.
The auditor may need more time to understand:
- Your ISMS design.
- Scope.
- Risk assessment.
- Statement of Applicability.
- Control implementation.
- Evidence structure.
- Internal processes.
If previous internal audits exist, provide their dates and explain whether earlier findings were closed.
6. Explain What You Want the Auditor to Cover
Do you need a full ISO 27001 internal audit?
Or do you need targeted testing?
A full certification-readiness audit may cover:
- ISO/IEC 27001:2022 requirements.
- Applicable Annex A controls.
- Your policies and procedures.
- Your Statement of Applicability.
A targeted audit may instead focus on:
7. Explain What Evidence Is Ready
You do not need to send every document when asking for a quote.
However, explain how mature your documentation is.
Our policies, risk register, Statement of Applicability, asset inventory, supplier register, procedures, and evidence are organized.
Our implementation is nearly complete, but some control evidence is still being collected.
8. Give a Short Technology Overview
You do not need to send a detailed architecture diagram for the initial quote request.
Instead, identify your major platforms.
| Area | Example Information |
|---|---|
| Productivity | Microsoft 365 |
| Identity | Microsoft Entra ID |
| Cloud | Azure / AWS |
| Endpoints | Intune-managed Windows devices |
| Development | GitHub / Azure DevOps |
| Security | Microsoft Defender / SIEM |
| Business Systems | CRM, HRIS, ticketing |
| Product | Cloud-hosted SaaS application |
9. Identify Important Suppliers
Supplier complexity can affect audit testing.
Tell the auditor if you depend heavily on:
- Cloud providers.
- Managed service providers.
- Software vendors.
- Data processors.
- Developers or contractors.
- Critical SaaS platforms.
10. Define Your Audit Expectations
Not every buyer expects the same deliverables.
Decide whether you need:
- An audit plan.
- Control-owner interviews.
- Evidence sampling.
- A detailed internal audit report.
- Nonconformity reporting.
- Observations and improvement opportunities.
- Corrective-action review.
- A follow-up or retest.
- Certification-readiness guidance.
What Should Be Included in an ISO 27001 Internal Audit Quote?
Do not compare proposals using price alone.
Look at what the engagement actually includes.
If the proposal only says:
Ask for more detail before deciding.
Does the Internal Auditor Need to Be Independent?
The audit process needs objectivity and impartiality.
That does not always mean the auditor must come from an external company.
However, auditors should not simply audit their own work without safeguards for objectivity.
For smaller organizations, outsourcing can be practical when no suitably independent internal resource exists.
What Should You Look for When Hiring an ISO 27001 Internal Auditor?
Price matters.
However, it should not be the only consideration.
Look for an auditor who can:
- Understand ISO/IEC 27001:2022.
- Evaluate technical and organizational evidence.
- Understand your type of environment.
- Communicate findings clearly.
- Support certification-readiness objectives.
- Maintain objectivity.
A useful audit report should explain:
- What was tested.
- What evidence was sampled.
- What did not conform.
- Why the issue matters.
- What needs attention before certification.
What Affects an ISO 27001 Internal Audit Proposal?
| Factor | Why It Matters |
|---|---|
| ISMS Scope | Defines what must be audited |
| Employee Count | Indicates organizational complexity |
| Locations | May add physical or regional testing |
| Technology | Affects technical audit complexity |
| Processes | Affects interviews and sampling |
| Suppliers | May increase third-party testing |
| ISMS Maturity | New implementations may require deeper review |
| Audit Type | Full audit requires more effort than targeted testing |
| Timeline | Affects scheduling and planning |
| Onsite Requirements | Travel may affect the engagement |
| Follow-Up Testing | Corrective-action retesting adds work |
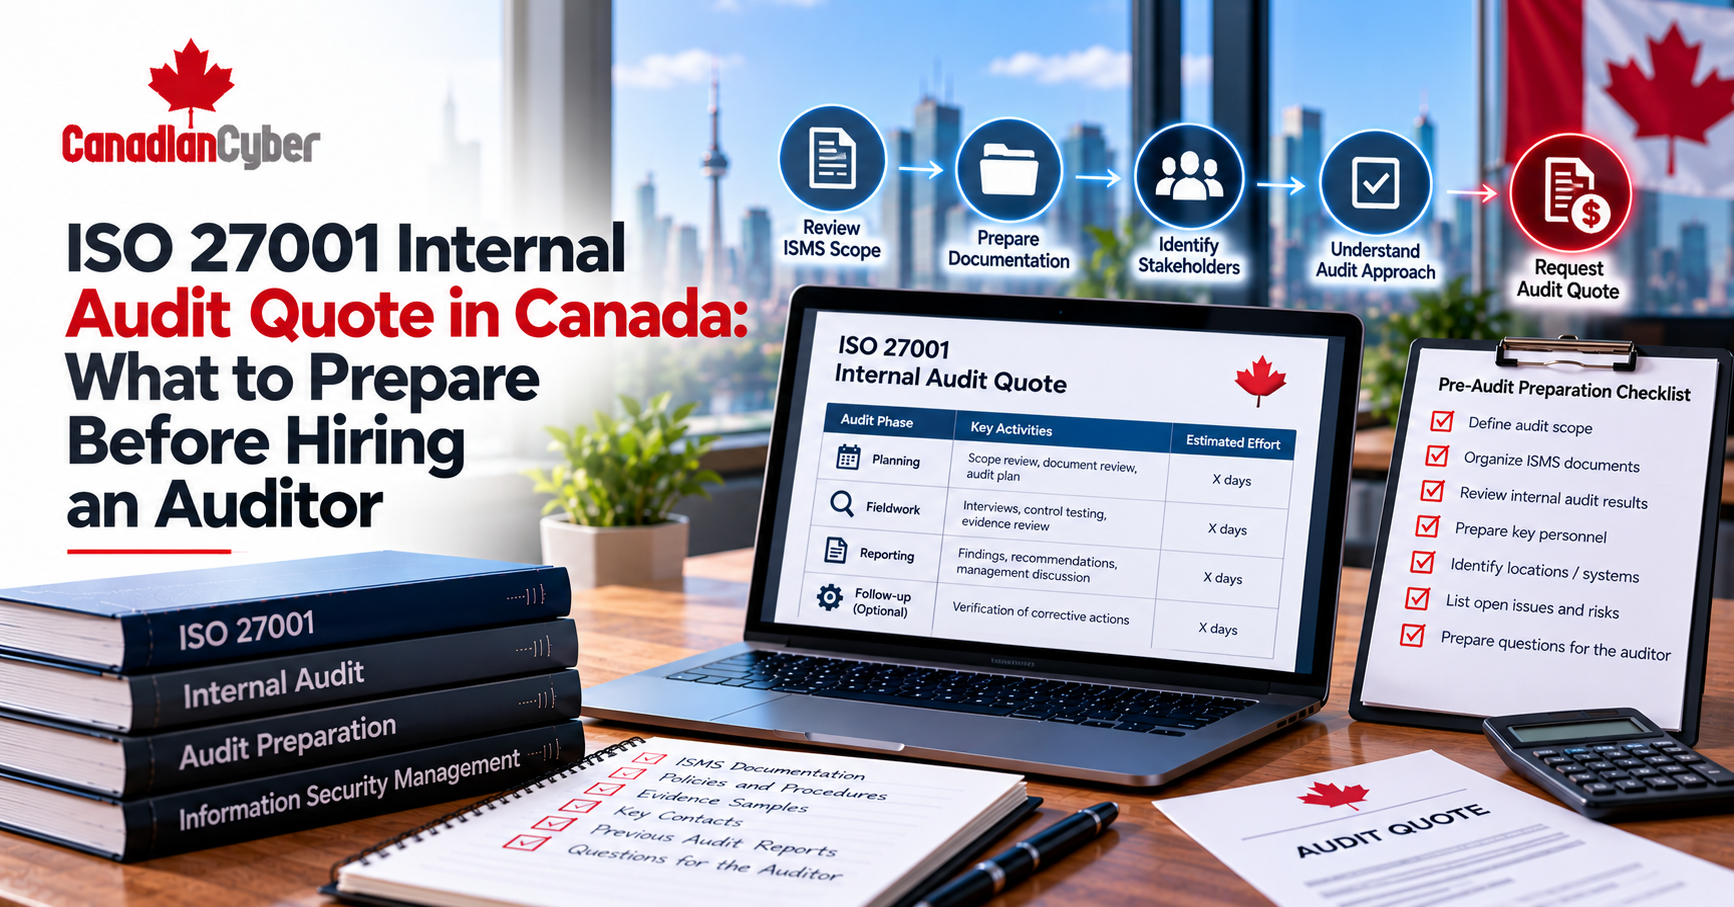
ISO 27001 Internal Audit Quote Request Checklist
Before contacting an auditor, prepare this simple checklist.
☐ Company name and industry
☐ Total employee count
☐ Employees within ISMS scope
☐ Current ISMS scope statement
☐ Office and operational locations
☐ Remote, hybrid, or onsite working model
☐ Main technology and cloud platforms
☐ Certification status
☐ Stage 1 / Stage 2 / surveillance / recertification date
☐ First internal audit or repeat audit
☐ Full or targeted audit required
☐ Remote or onsite preference
☐ Major suppliers or outsourced services
☐ Documentation and evidence readiness
☐ Required audit deliverables
☐ Corrective-action follow-up or retesting needed
Have This Information Ready?
You do not need every detail to be perfect. Send Canadian Cyber what you already know, and use the quote discussion to clarify the remaining scope.
Request Your ISO 27001 Internal Audit Quote from Canadian Cyber
Example ISO 27001 Internal Audit Quote Request
A useful initial request could look like this:
We are a Canadian SaaS company with 75 employees. Approximately 55 employees are within our ISO 27001 ISMS scope.
Our environment includes Microsoft 365, Entra ID, Azure, GitHub, and a cloud-hosted SaaS platform.
We operate primarily remotely with a small Toronto office. This is our first ISO 27001 certification, and Stage 1 is planned for February 2027.
Our risk assessment, Statement of Applicability, policies, supplier register, asset inventory, and most control evidence are complete.
We need an independent full-scope ISO 27001:2022 internal audit with interviews, evidence sampling, a report, findings, and corrective-action recommendations. Please provide a proposal and let us know what additional information you require.
Frequently Asked Questions
How much does an ISO 27001 internal audit cost in Canada?
Cost depends on scope, complexity, employees, locations, technology, audit depth, timeline, delivery method, and required deliverables.
What information do I need for an ISO 27001 internal audit quote?
At minimum, provide your ISMS scope, employee count, locations, certification timeline, and audit expectations.
Can an ISO 27001 internal audit be done remotely?
Many activities can be completed remotely. The appropriate approach depends on your scope, physical environment, objectives, and agreed audit plan.
How long before certification should we arrange the internal audit?
Allow enough time to complete the audit, address findings, verify important corrective actions, and complete related certification-readiness activities.
Can the same consultant who implemented our ISMS audit it?
Objectivity and impartiality must be protected. Consider whether the auditor was directly responsible for designing or implementing the work being audited.
Do we need to send every ISO 27001 document before getting a quote?
Usually not. Initial scoping can begin with high-level information before detailed evidence is requested.
What happens after we accept the quote?
Typical next steps include confirming scope, scheduling interviews, requesting evidence, conducting audit testing, reporting findings, and addressing follow-up actions.
The Takeaway
If you need an ISO 27001 internal audit quote, do not begin only with:
Instead, begin with:
Prepare your:
That gives an auditor enough context to understand the engagement.
A good internal audit should tell you where your ISMS works, where gaps remain, and what needs attention before certification.
Need an ISO 27001 Internal Audit Quote in Canada?
Canadian Cyber provides ISO 27001 internal audit services for organizations preparing for certification and businesses that need an independent review of their existing ISMS.
Send your ISMS scope, employee count, locations, certification timeline, and audit expectations to start the discussion.
Request Your ISO 27001 Internal Audit Quote from Canadian Cyber
Stay Connected With Canadian Cyber
Follow Canadian Cyber for practical guidance on ISO 27001 internal audits, certification readiness, audit evidence, risk management, and ISMS improvement.